
Nummyx is a security research company working on Bitcoin and the systems built on it.
Services
Who we work with
Custodians, exchanges, trading desks, and corporate treasuries
Key material in hardware security modules (HSM) and secure enclaves. Multisig and multi-party threshold signing (MPC). Hot, warm, and cold wallets. Transaction authorization policy, the path from request to signature, key ceremonies, backup and recovery paths. What survives a compromised host, what a malicious hypervisor observes, what remains in memory, and what a rogue operator can reach.Hardware wallet and signing device vendors
Secure elements and the hardware-software boundary. Fault injection, side channels, and debug interfaces. Secure boot, firmware update and rollback paths. Entropy and seed generation, provisioning and supply chain, input paths over QR, microSD, NFC, and Bluetooth. What physical access alone buys an attacker, what the computer it talks to can push through those paths, whether the screen shows what gets signed, and whether the firmware uses the chip as its datasheet specifies.Sidechains and L2s: channels, statechains, and rollups teams
Peg custody, federations, and threshold signers. Fraud proofs, challenge protocols, and revocation penalties. Peg-in and peg-out validation, data availability, censorship and liveness assumptions. Timelocks, exit windows, and emergency recovery paths. What signers can do if enough of them collude, whether a user can exit when the operator stops cooperating, and whether that exit confirms before its timelock expires.
What we look at
Protocol logic and state machines
Adversarial review of the design, the specification, and the code. Trust boundaries, economic and timing assumptions, failure modes under adversarial conditions, reachable states the design never intended, what the spec leaves undefined, and where code and spec disagree.Cryptographic implementations
Implementation review of signing and key derivation. Privacy, zero-knowledge proofs, and post-quantum schemes. Nonce handling, threshold and multisignature code, constant-time behavior and side channels.
How we work
There are no secure systems, but attackers also have constraints. They work to deadlines and budgets. We work to raise the cost of an attack so that they go looking elsewhere.
We start by understanding the needs of each client. There are no one-size-fits-all solutions here. We pride ourselves on deeply studying the domain and a particular implementation. We read papers and technical documents. We look at code, including the binary code that actually runs on devices, and the infrastructure around it.
Like an advanced attacker would, we map the target first, then explore it systematically. We use manual review, static analysis, fuzzing, race detection, symbolic execution, formal verification, and differential testing. We create bespoke tooling and harnesses as part of an engagement. We build explainable tools, not black boxes. Our manual review process is streamlined to help us triage issues faster.
Our goal is to improve your security posture. The outcome is not just a report of findings, but the tools we built as part of the project, and what your engineers learn from the work.
About
Meet the founder
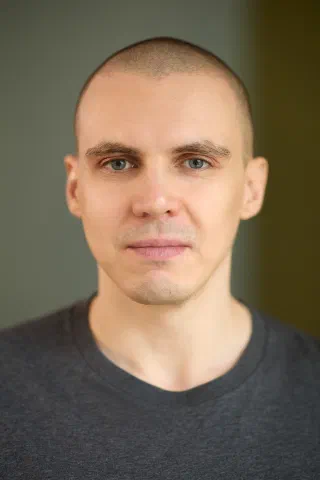
Nikita Karetnikov
Founder & CEO
Nikita spent the majority of his career in security R&D, building bespoke tooling. He was part of a team developing a security-focused hypervisor, worked on a CPU emulator and symbolic execution engine for vulnerability research, created fuzzers, performed reverse engineering, contributed to a concurrency race detection framework, and was a core engineer in a memory forensics startup that later got acquired.
He also worked on the PyTorch compiler and currently leads an applied AI team at a major European bank.
Nikita founded Nummyx in 2026, to apply his security and AI expertise to Bitcoin.
Recent articles
Research and writing on Bitcoin security.